
Design Ideas for Creating a Home Office in Luxury Apartments
August 8, 2026
Android Multi Tool Software: A Complete Guide
August 10, 2026
A Software Update Point is one of the most important site system roles inside Microsoft Configuration Manager, and it works closely with Windows Server Update Services to keep every device in an organization protected against security risks. Without a properly configured Software Update Point, IT teams would struggle to deliver updates consistently across hundreds or thousands of machines.
This role acts as the communication bridge between Microsoft’s update catalog and the client computers spread across a company network. In simple words, it collects update information, stores it, and then makes sure the right updates reach the right devices at the right time.
Introduction to Software Update Point
Before diving into technical details, it is important to understand what a Software Update Point actually means and why organizations rely on it so heavily. This section explains the basic concept, its purpose, and its connection with WSUS.
What is a Software Update Point (SUP)
A Software Update Point is a site system role within Configuration Manager that manages the process of finding, downloading, and distributing software updates to client machines.
It does not create updates on its own; instead, it pulls update metadata from Microsoft and organizes it so that Configuration Manager can evaluate which devices need which patches. Think of it as a librarian who knows exactly which book is needed by which reader and arranges it accordingly.
Role of SUP in Configuration Manager (SCCM/MECM)
Inside Configuration Manager, the Software Update Point works as the central engine for patch management. It allows administrators to scan client compliance, group updates together, and push them out using deployment rules.
Without this role enabled, Configuration Manager cannot perform any update-related scanning or deployment activity across the environment.
Relationship Between SUP and WSUS
The Software Update Point cannot function alone; it depends entirely on Windows Server Update Services to operate. WSUS acts as the underlying engine that talks to
Microsoft Update servers, while the Software Update Point acts as the management layer on top of WSUS inside Configuration Manager. Together, they form a complete patching solution used by enterprises worldwide.
Why Software Updates Are Important in IT Infrastructure
Regular software updates protect systems from security vulnerabilities, improve performance, and fix known bugs. Organizations that fail to patch their systems on time often become easy targets for cyberattacks.
This is exactly why a properly functioning Software Update Point is treated as a critical part of enterprise IT security strategy rather than just an optional maintenance task.
Architecture and Components
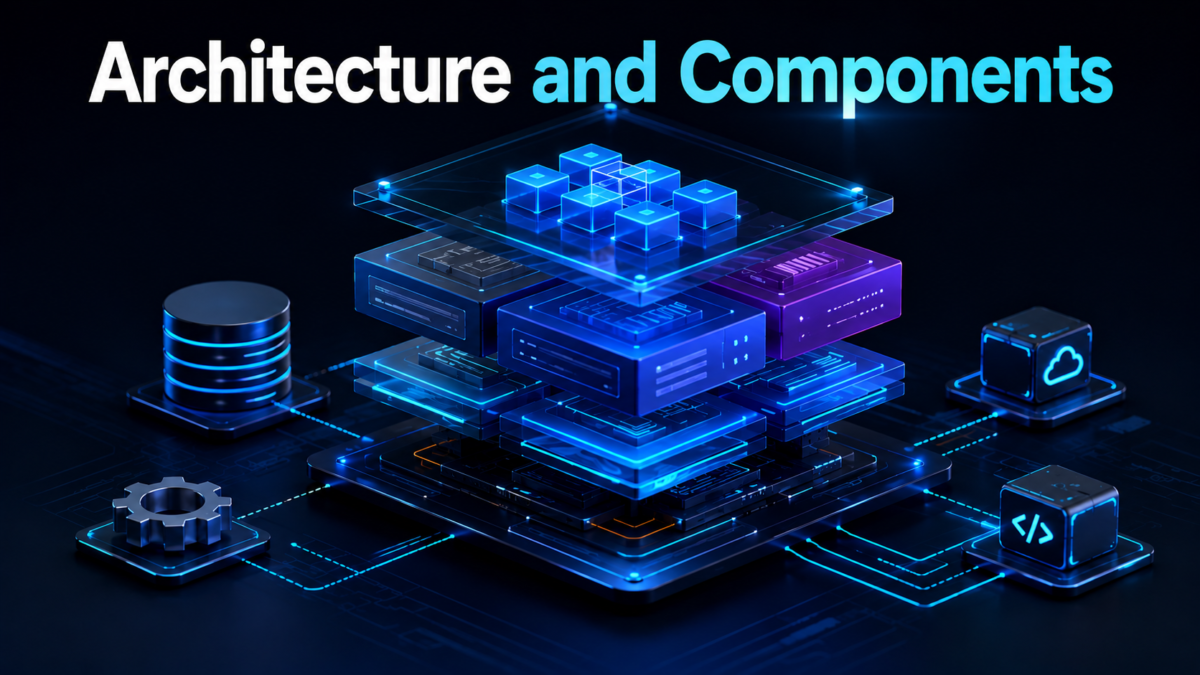
Understanding the internal architecture of a Software Update Point helps administrators troubleshoot issues faster and plan deployments more effectively. This section covers the key building blocks that make the role function correctly.
SUP as a Site System Role
The Software Update Point is installed as a site system role on a server that is already part of the Configuration Manager hierarchy. During installation, administrators choose which server will host this role, and Configuration Manager then configures it to communicate with WSUS automatically.
WSUS Server Components
WSUS itself is made up of several parts, including the WSUS Administration Console, the Update Services database, and the content storage location where update files are kept.
The Software Update Point interacts with all these parts to pull the required information into Configuration Manager.
WSUS Database (SUSDB)
The WSUS database, commonly known as SUSDB, stores metadata about updates, computer groups, and synchronization history.
This database can be hosted using Windows Internal Database or a full SQL Server instance, depending on the size of the environment and expected performance needs.
IIS (Internet Information Services) Dependency
WSUS relies on IIS to host its web services, which the Software Update Point uses to communicate with WSUS. If IIS is misconfigured or not running properly, the Software Update Point will fail to synchronize or deliver updates correctly.
Communication Flow Between SUP, WSUS, and Clients
The communication flow begins when the Software Update Point syncs with WSUS, WSUS syncs with Microsoft Update, and then client computers scan against the Software Update Point to check their compliance status.
This layered flow ensures accuracy and keeps the update process organized from top to bottom.
How Software Update Point Works
This section explains the actual working mechanism of the Software Update Point, including how updates are pulled, categorized, and made available to client devices across the network.
Syncing Updates from Microsoft Update Catalog
The Software Update Point periodically connects to the Microsoft Update Catalog to check for newly released updates.
During this synchronization process, metadata about each update, such as its title, description, and applicability rules, is downloaded and stored locally for further processing.
Metadata vs Actual Update Files
It is important to understand that synchronization only downloads metadata, not the actual update files. The real update files, also called binaries, are downloaded separately only when an administrator creates a deployment, which helps save bandwidth and storage space until updates are actually needed.
Update Categories and Classifications
Updates are organized into classifications such as security updates, critical updates, feature packs, and update rollups.
Administrators can choose specific classifications during configuration so that only relevant update types are synchronized instead of pulling everything available.
Product Categories (OS versions, Office, etc.)
Along with classifications, updates are also grouped by product categories such as specific Windows operating system versions or Microsoft Office editions.
This allows administrators to narrow down synchronization to only the products actually used within their organization.
Synchronization Schedule
Administrators can configure a synchronization schedule so that the Software Update Point automatically checks for new updates at regular intervals, such as daily or weekly.
A consistent schedule ensures that the environment always has access to the latest available patches without manual intervention.
Types of SUP Deployment
Depending on the size and structure of an organization, the Software Update Point can be deployed in different ways. This section explains the common deployment models used in real-world environments.
Single SUP Setup
In smaller environments, a single Software Update Point is often enough to handle all synchronization and deployment tasks. This setup is simple to manage and works well when the number of client computers is relatively limited.
Multiple SUPs for Load Balancing
Larger organizations often deploy multiple Software Update Points to distribute the load of client scanning and content delivery. This approach improves performance and provides redundancy in case one server becomes temporarily unavailable.
SUP in Hierarchy (Central Administration Site, Primary, Secondary)
In a multi-site Configuration Manager hierarchy, the Software Update Point can be installed at the Central Administration Site, Primary Site, or Secondary Site level.
Each level plays a role in ensuring updates flow smoothly from the top of the hierarchy down to individual client devices.
SUP for Internet-Based Clients
Organizations with remote or traveling employees often configure a Software Update Point that supports internet-based client management. This allows devices outside the corporate network to still receive updates securely without needing a direct connection to internal servers.
Installation and Configuration
Setting up a Software Update Point involves several prerequisites and configuration steps. This section walks through the essential requirements and the general process administrators follow.
Prerequisites (WSUS Role, IIS, SQL Server)
Before installing the Software Update Point, the server must already have the WSUS role and IIS installed and properly configured.
Depending on the expected load, a SQL Server instance may also be required instead of relying on the default internal database.
Step-by-Step Installation Process
The installation process generally begins by adding the Software Update Point role through the Configuration Manager console, selecting the target server, and specifying the WSUS port settings.
Once installed, Configuration Manager automatically links the role to the underlying WSUS instance for management.
Configuring Sync Source
Administrators need to define where the Software Update Point pulls its updates from, which is typically Microsoft Update, though in some hierarchies it may sync from an upstream Software Update Point instead. This setting determines the origin point of all update metadata.
Configuring Products and Classifications
After installation, administrators select which product categories and update classifications should be synchronized.
This step is important because selecting too many categories can slow down synchronization and consume unnecessary storage space.
Setting Sync Schedule
The final configuration step usually involves setting how often synchronization should occur. Many organizations choose a nightly or weekly schedule to balance timely updates with system performance.
Software Update Management Workflow
Once the Software Update Point is configured, administrators follow a structured workflow to actually deliver updates to client machines. This section explains the key stages of that workflow.
Creating Software Update Groups
Software update groups allow administrators to bundle multiple related updates together for easier management. Instead of deploying updates one by one, an entire group can be deployed at once, which saves significant time and effort.
Deployment Packages
Deployment packages contain the actual update files that need to be downloaded to a distribution point before clients can install them.
Creating a well-organized deployment package ensures that content is available close to the client devices that need it.
Automatic Deployment Rules (ADRs)
Automatic Deployment Rules allow administrators to automate the process of approving and deploying new updates based on predefined criteria. This reduces manual work significantly, especially for routine monthly security patches.
Maintenance Windows
Maintenance windows define specific time periods during which updates are allowed to install on client machines.
This prevents disruptive restarts or installations during working hours and keeps productivity unaffected.
Compliance Monitoring and Reporting
After deployment, administrators use built-in reports to monitor how many devices successfully installed the updates and which ones failed. This visibility helps IT teams quickly identify problem areas and take corrective action.
Client-Side Interaction
The Software Update Point does not just manage updates on the server side; it also directly interacts with client computers throughout the scanning and deployment process. This section explains that client-side experience.
Client Scan for Updates
Client computers regularly scan against the Software Update Point to check their current compliance status. During this scan, the client compares its installed updates against the available update catalog to determine what is missing.
Update Deployment to Clients
Once a deployment is created, targeted client machines download the required update files from their assigned distribution point and begin the installation process according to the configured deadline and settings.
Reboot Behavior and Notifications
Many updates require a system restart to complete installation. Configuration Manager typically notifies users before a scheduled reboot, giving them a chance to save their work, unless the organization enforces a stricter forced restart policy.
Troubleshooting Client Scan Failures
Sometimes client machines fail to scan successfully due to connectivity issues, incorrect WSUS settings, or corrupted update agent components. Administrators usually resolve these issues by checking client logs and re-running the update scan cycle manually.
Common Issues and Troubleshooting
Like any enterprise system, the Software Update Point can run into technical problems from time to time. This section highlights the most common issues administrators face and how they are typically diagnosed.
Sync Failures
Synchronization failures often occur due to network connectivity problems, proxy misconfigurations, or issues reaching Microsoft Update servers. Checking the synchronization logs is usually the first step in identifying the root cause.
WSUS Content Not Downloading
Sometimes update metadata syncs successfully, but the actual content files fail to download to distribution points. This is often caused by insufficient disk space, incorrect content library paths, or firewall restrictions blocking the download process.
WSUS Console Errors (e.g., “WSUS server not configured”)
This particular error usually appears when the WSUS role has not been fully configured or when there is a version mismatch between WSUS and Configuration Manager. Reviewing the WSUS configuration wizard settings often resolves this issue.
Log Files to Check (WCM.log, WSUSCtrl.log, WSyncMgr.log)
Configuration Manager maintains dedicated log files that record detailed information about Software Update Point activity. Reviewing these logs allows administrators to pinpoint exactly where a failure occurred instead of guessing at the cause.
| Log File | Purpose |
| WCM.log | Tracks component installation and configuration changes for the SUP role |
| WSUSCtrl.log | Records communication status between Configuration Manager and the WSUS server |
| WSyncMgr.log | Logs the synchronization process, including success or failure of update sync cycles |
Best Practices
Following recommended best practices helps organizations get the most reliable performance out of their Software Update Point setup. This section lists practical tips that experienced administrators commonly apply.
Planning SUP Placement in Large Environments
In large organizations, it is important to carefully plan where each Software Update Point is placed within the hierarchy to avoid unnecessary network traffic and to ensure faster scanning for client devices located in different regions.
Regular Maintenance of WSUS Database
The WSUS database should be maintained regularly by running recommended maintenance scripts, since an overloaded database can significantly slow down synchronization and client scanning performance over time.
Cleanup of Obsolete Updates
Removing outdated or superseded updates from the WSUS console helps keep the database lean and improves overall system responsiveness. Many administrators schedule this cleanup task on a monthly basis.
Security Considerations
Since the Software Update Point handles critical patching for an entire organization, it should be secured properly with restricted administrative access, updated server software, and monitored network traffic to prevent unauthorized changes.
• Restrict administrative access to the SUP server to authorized personnel only
• Keep the underlying WSUS and IIS components patched and updated
• Monitor synchronization logs regularly for unusual activity
• Use SSL where possible for secure communication with clients
Conclusion
The Software Update Point remains one of the most essential roles within Configuration Manager for maintaining a secure and well-patched IT environment. By understanding its architecture, working mechanism, deployment workflow, and common troubleshooting steps, administrators can ensure smoother patch management across their organization.
A properly planned and maintained Software Update Point ultimately reduces security risks, improves compliance visibility, and keeps enterprise systems running efficiently without unnecessary manual effort.
Frequently Asked Questions
Is Software Update Point the same as WSUS?
No, they are related but not identical. WSUS is the underlying update engine, while the Software Update Point is the Configuration Manager role that manages and controls WSUS for enterprise deployment purposes.
Can an organization have more than one Software Update Point?
Yes, larger organizations often deploy multiple Software Update Points across their hierarchy to balance client load and provide redundancy in case one server experiences downtime.
What happens if the Software Update Point stops working?
If the Software Update Point becomes unavailable, client machines will be unable to scan for compliance or receive new update deployments until the role is restored and functioning correctly again.
Related Articles
Aula F75 Software: Complete Download, Install & Setup Guide
Drake Software Login: The Complete Guide to Access, Setup & Troubleshooting
Golf Simulator Software: The Complete Guide
Best Property Management Software: A Complete Guide for Landlords and Property Managers
How to Classify Software Application Components: Complete Guide


